Email Security Blog
Expert insights on email authentication, threat intelligence, and protecting your business from email fraud
Featured Article
Cybersecurity Awareness Month 2026: Is Your Email Domain Making It Easy for Scammers?
This year's Cybersecurity Awareness Month theme is "Don't Make It Easy for Them." For a business, an email domain anyone can forge is one of the easiest openings. Here's how to close it.
Read ArticleAll Articles
Zendesk Now Checks SPF and DKIM by Default: Will Your Emails Still Get Through?
Zendesk is making inbound sender authentication the default. Email that fails SPF with missing or failed DKIM can be suspended. Here's what senders and Zendesk admins should check now.
Can DMARC stop lookalike email scams? Lessons from a $158,000 strawberry-seed fraud
An agricultural company wired $158,000 after a payment request from a near-identical copy of its seed supplier's email address. What DMARC does and doesn't stop, and how to verify vendor payments.
Would DMARC stop a fake CEO invoice? Inside the million-email ACH scam
In early August, attackers sent over a million emails in which 'the CEO' approved a fake ServiceNow invoice. Microsoft disclosed it on Sep 10. What DMARC can't see, and an AP verification playbook.
What is ASCII smuggling? The invisible-letter trick hiding phishing from filters
Microsoft says a phishing campaign slipped invisible Unicode 'tag' characters inside words like 'funding' so filters would miss them. How the trick works and what small businesses should do.
Can DMARC stop lookalike-domain fraud? Lessons from the $7.5M charity BEC case
A man who used lookalike domains and hijacked mailboxes in a scheme against two charities that diverted more than $7.5M got 8 years. What DMARC stops, what it doesn't, and how to verify payment requests.
Zimbra flaw CVE-2026-73570 is under attack: what should small businesses do?
CISA confirmed on August 21 that attackers are exploiting Zimbra mail-server flaw CVE-2026-73570. Why a hacked mail server can send 'authenticated' email as you, and what to do.
Run Exchange Server or Outlook 2016? What Microsoft's August 2026 Updates Fix
Microsoft's August 11, 2026 updates fix seven Exchange Server vulnerabilities, permanently disable OWA Light and patch an Outlook 2016 spoofing flaw. Here's who needs them and how to install safely.
Can an Email Steal Your Password With No Link or Attachment? Black Hat's 'CSS Bomb'
Research shown at Black Hat USA 2026 used nothing but an email's styling code to draw a fake login box and record keystrokes inside webmail. Here's how it works and the one habit that beats it.
Is Phishing Still the #1 Way Attackers Get In? What Talos and IBM Found in July 2026
Two July 2026 reports agree: phishing is still the main way attackers get in, and they increasingly plan for MFA. What Cisco Talos and IBM found, and what small businesses should do.
If a Scam Email Passes SPF and DKIM, Is It Legit? What Microsoft's Q2 Report Shows
Microsoft's Q2 2026 report describes a BEC campaign that passed SPF and achieved DKIM alignment. Here's what email authentication proves, what it doesn't, and what helps stop these scams.
Is Microsoft Ending Text-Message MFA? Passkeys Will Be the Entra ID Default
Microsoft will start rolling out passkeys as the Entra ID default on September 1, 2026 and stop providing SMS and voice MFA on February 1, 2027. Here's why it matters for BEC and what small businesses should do now.
Do BEC Scammers Get Caught? What INTERPOL's 5,811 Arrests Mean for Your Business
INTERPOL's Operation First Light 2026 led to 5,811 arrests and USD 293 million intercepted, with BEC among the targeted scams. Arrests help, but prevention is what protects your money.
Does Microsoft 365 E3 Now Include Defender for Office 365? What Changed on July 1
From July 1, 2026, Office 365 E3 and Microsoft 365 E3 include Defender for Office 365 Plan 1. Here's who is affected, what to turn on first, and what it still doesn't do for spoofing.
Email Authentication Requirements in 2026: What Google, Yahoo, and Microsoft Now Demand
The era of optional email authentication is over. Google and Yahoo started enforcing sender requirements in 2024, Microsoft followed in 2025, and in 2026 unauthenticated email is increasingly filtered or rejected outright. Here is exactly what the big mailbox providers require now.
Email Security Compliance in 2026: HIPAA, PCI DSS 4.0, GDPR, and New Mandates
Regulatory pressure on email security is intensifying in 2026. From HIPAA to PCI DSS 4.0 to GDPR, here is what every industry must know about email authentication compliance.
Cyber Insurance and Email Authentication: Why Your Policy May Require DMARC in 2026
Cyber insurance carriers are making email authentication a policy requirement. If your DMARC is not at enforcement, you could face higher premiums or denied claims in 2026.
RAT Malware Delivered by Email: How Remote Access Trojans Are Evolving in 2026
Remote Access Trojans delivered through email remain one of the most dangerous cyber threats in 2026. AI-generated lures and novel evasion techniques are making RATs harder to detect than ever.
From p=none to p=reject: The Complete DMARC Enforcement Journey in 2026
Most organizations get stuck at DMARC p=none. This guide walks you through the complete journey to p=reject enforcement without breaking your email delivery.
The 2026 Small Business Email Security Checklist: 15 Steps to Full Protection
Small businesses are the #1 target for email fraud. This 15-step checklist gives you everything you need to fully protect your business email in 2026, with free tools and clear instructions.
Defending Against AI-Powered Phishing: A 2026 Survival Guide
AI-generated phishing emails are now virtually indistinguishable from legitimate messages. Here is your complete 2026 defense playbook against the most sophisticated email threats ever seen.
2026 Email Security Predictions: AI Threats, Zero Trust, and What Your Business Must Do Now
As we enter 2026, the email threat landscape is evolving faster than ever. AI-generated phishing, zero trust mandates, and universal DMARC enforcement are reshaping how businesses must approach email security.
Microsoft 365 Enforces Bulk Sender Authentication: May 2025 Deadline
Microsoft is enforcing strict email authentication requirements for bulk senders starting May 2025. Organizations sending 5,000+ emails daily must implement SPF, DKIM, and DMARC or face delivery failures.
BEC Attacks in 2025: Billions Lost to Email Fraud Every Year
Business Email Compromise remains one of the costliest cybercrimes tracked by the FBI, with billions in reported losses every year. Understanding and preventing BEC is more critical than ever.
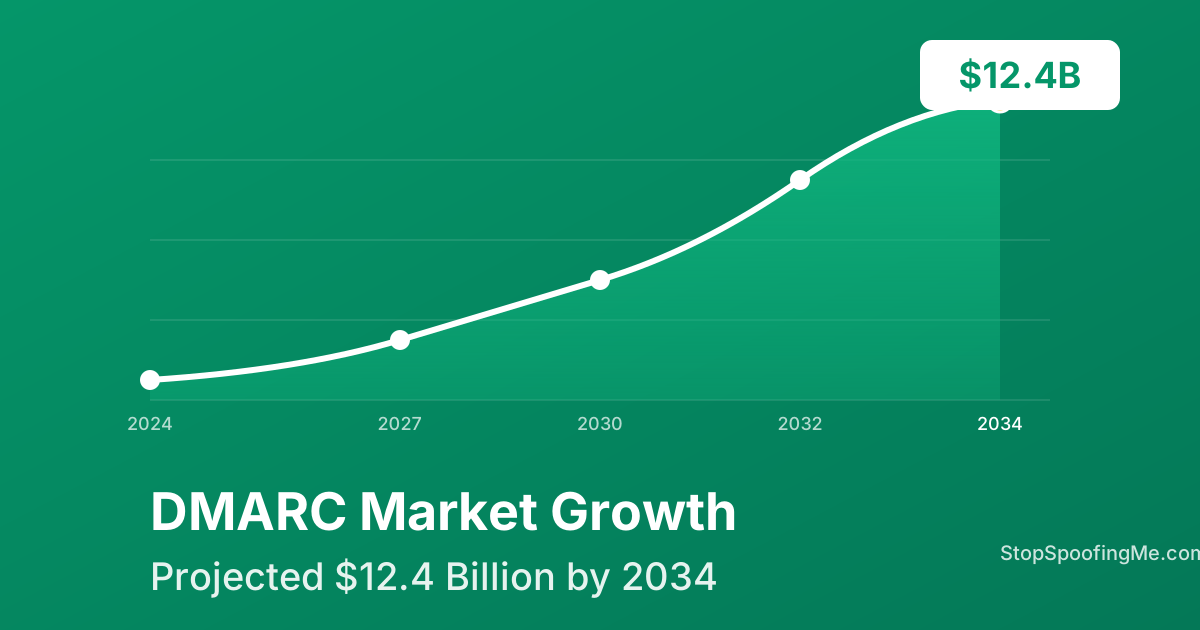
DMARC Market Explodes to $12.4 Billion by 2034: Why Enterprises Are Racing to Authenticate
The global DMARC market is projected to reach $12.4 billion by 2034, growing at 18.6% CAGR. Enterprise adoption is accelerating as organizations recognize the ROI of email authentication.
Microsoft 365 Direct Send Exploit: How Attackers Bypass Email Authentication
A Microsoft 365 configuration feature called "Direct Send" can be exploited by attackers to bypass email authentication. Learn how this works and how to protect your organization.
The Complete 2025 Guide to Google & Yahoo Bulk Sender Rules
A comprehensive guide to Google and Yahoo's bulk sender requirements. Learn about authentication, unsubscribe mechanisms, spam thresholds, and how to maintain compliance in 2025.
BIMI in 2025: Why Your Logo in Inboxes Matters More Than Ever
BIMI displays your brand logo next to emails in supported inboxes. With DMARC enforcement becoming mandatory, 2025 is the perfect time to implement BIMI for enhanced brand trust.
What is an SPF Record? Complete Guide to Email Authentication
SPF (Sender Policy Framework) records are crucial for preventing email spoofing. Learn what they are, why you need them, and how to set them up correctly.
DMARC Setup Guide (2026): How to Get From p=none to Enforcement Safely
How to set up DMARC without blocking your own mail: list your senders, align SPF and DKIM, read the reports, then enforce. Updated for RFC 9989, which replaced RFC 7489 in May 2026.
7 Ways to Prevent Email Spoofing and Protect Your Brand
Seven practical defenses against email spoofing and impersonation, and what each one does and doesn't stop, from DMARC enforcement and parked-domain lockdown to call-back checks and passkeys.
Stay Updated on Email Security
Get the latest email security insights, threat alerts, and best practices delivered to your inbox.
Subscribe to Updates